Unclear ownership
Nobody can say who signs off an AI decision.
Governance at Execution™
Helping organisations assess, govern, operate and assure AI safely, responsibly and at scale.
Free to start. No card required. Full policy pack from £79.
Built for UK small and medium businesses navigating UK GDPR, the EU AI Act, and sector-specific AI rules.
The business problem
Nobody can say who signs off an AI decision.
Policy exists on paper, not in the workflow.
The tools in daily use were never written down.
No named person behind a system's actions.
No one watches what changes after go-live.
UK GDPR, the EU AI Act and sector rules grow.
Most AI challenges are not technology challenges. They're governance and readiness challenges.
One structured path from first assessment to certification readiness. Each stage builds on the last — you always know where you stand and what comes next.
A free readiness call maps where you stand on the path and what the next stage looks like for your business.
Book a Readiness Assessment →Map the AI tools your teams actually use, the data they touch and the rules that reach them.
Click to learn more →Turn that picture into structure: ownership, policy, risk classification and clear decision rights.
Click to learn more →Trace every AI action to the person or process that authorised it, with boundaries and evidence.
Click to learn more →At the point of action, confirm authority is still valid, the action is in scope and conditions allow it.
Click to learn more →Run approvals, registers and records inside everyday work — not in a binder on a shelf.
Click to learn more →Re-check the controls as tools, data and rules change, and keep the evidence as you go.
Click to learn more →Walk into an ISO 42001 audit or customer due diligence with evidence already in order.
Click to learn more →The Diagnostic™
Before anything is designed or deployed, you need a measured view of where you stand. The Trestano AI Governance & Readiness Diagnostic™ scores your organisation, shows where the exposure sits, and hands you a report your leadership can act on.
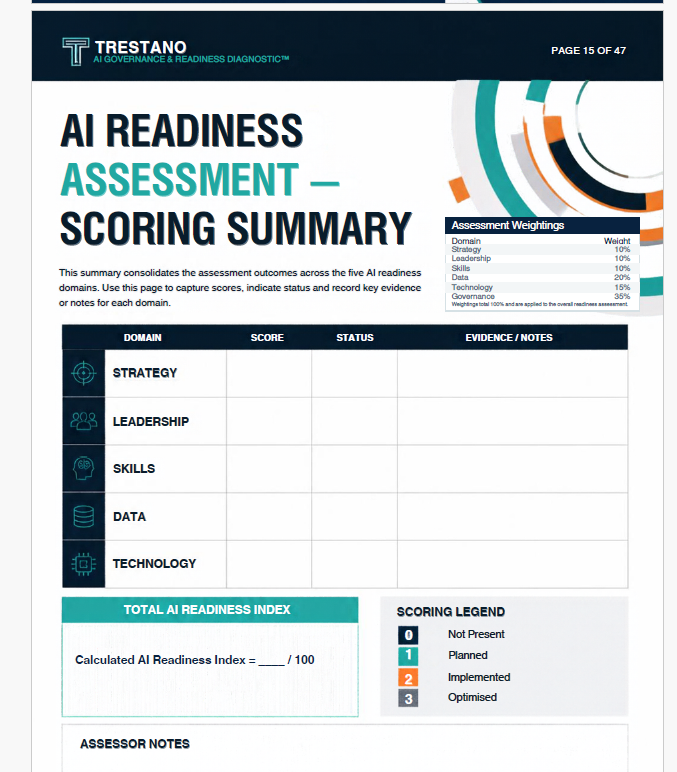
Sample format of the Scoring Summary — the readiness scorecard produced with every full diagnostic. Illustrative formats only — your diagnostic is scored and written for your organisation.
Book a Diagnostic and we walk your leadership through the results, the gaps that matter first, and the shortest credible path to certification readiness.
Outcomes, not theory
Understand organisational capability.
Define ownership and accountability.
Define who authorised AI to act.
Validate decisions in real time.
Manage AI safely once deployed.
Monitor, review and improve.
Prepare for ISO 42001 and future regulation.
The blueprint
Eight connected layers, from business intent to certification readiness. Each layer rests on the one above it and feeds the one below — designed once, owned at every layer, and holding under audit.
Explore the full model →The eight layers
Governance Operations™
Policy tells people what should happen. Operations decide what does — a continuous cycle that finds the AI in use, judges it, acts on it, and comes back stronger each time.
The outcomes
In practice
Every engagement is reported the same way, so the result is always visible end to end.
These are written scenarios, not client accounts — shared to show how the same situations get solved.
Example 1
SME using AI without governance
1Challenge
A 15-person HR consultancy used AI-powered features inside their email platform, CRM, and scheduling tools — but didn’t consider any of it “AI use.” When a client asked for evidence of AI controls, they had nothing documented.
2Findings
A simple AI register surfaced nine tools with embedded AI, none of them documented or assessed.
3Actions
Each tool was registered, evidence was produced for every one, and a governance foundation was put in place.
4Outcomes
Defensible documentation and a clear governance foundation. The client’s evidence request was answered within a week, and client confidence increased immediately.
9
AI tools identified and registered
5 days
Saved vs. building evidence manually
100%
Of embedded AI features documented
1 week
To answer the client’s evidence request
Illustrative figures from a written scenario, not a client result — shown to indicate the kind of measurable outcome Trestano engagements are designed to produce.
Example 2
Preparing for ISO/IEC 42001
1Challenge
A 40-person software supplier was told that ISO/IEC 42001 evidence would form part of its next contract renewal. Policies sat in a folder, but there was no AI register, no risk assessment and no internal audit — nothing that behaved like a management system.
2Findings
A gap review against the standard found six areas of work missing: documented scope, leadership accountability, an AI risk assessment and statement of applicability, lifecycle controls, internal audit, and corrective action.
3Actions
All six were delivered as one engagement — scope and AI register written, owners named, risks rated and treated, lifecycle controls documented, a first internal audit run, and its findings closed out with evidence.
4Outcomes
A management system that can be shown to an auditor, the renewal condition met, and staff able to answer audit questions from documents they had written themselves.
6
Areas of work closed against the standard
9 weeks
From gap review to an audit-ready system
0
Major nonconformities at the first internal audit
1
Contract renewal condition met
Illustrative figures from a written scenario, not a client result — shown to indicate the kind of measurable outcome Trestano engagements are designed to produce.
Example 3
Deploying AI agents or automation
1Challenge
A 25-person property management firm rolled out AI agents that draft and send tenant emails, chase payments and update records automatically. No one had decided what the agent could do on its own, or when a person had to step in.
2Findings
The agent could act on any record, with no approval boundary, no escalation threshold and no log of what it had already done — so a wrong action would neither be detected nor reversed.
3Actions
Execution boundaries were written for the agent, escalation thresholds agreed with named owners, an authority check placed in front of every high-impact action, and each action logged as evidence.
4Outcomes
The agent kept working at speed inside agreed limits, staff knew what it could and could not do, and every automated action traced back to the person who authorised it.
4
High-impact actions now requiring human approval
100%
Of agent actions logged against a named authority
3
Escalation thresholds agreed with named owners
0
Unauthorised agent actions since controls went live
Illustrative figures from a written scenario, not a client result — shown to indicate the kind of measurable outcome Trestano engagements are designed to produce.
Glen Jones
Founder, Trestano Ltd
Trestano is a UK company built for small and medium-sized businesses that use AI and need to be able to prove how they govern it.
More about TrestanoAbout Trestano
Trestano started with a moment that kept repeating: sitting with owners of good, sensible businesses as they realised their teams were using AI tools nobody had approved, nobody had documented, and nobody could now account for — and watching the confidence drain out of the room when a client, an insurer or a tender asked the one question they couldn't answer.
The tools were never the problem. The silence around them was. Again and again it wasn't recklessness — it was that the help available was written for companies with legal departments, while the businesses in front of me had an ops lead doing three jobs.
So I built Trestano: the same defensible picture of AI use that a large enterprise takes for granted, without the six-week onboarding or the six-figure invoice. One methodology, fixed fees, and documentation you can hand to anyone who asks.
If you can't say who authorised your AI to do what it just did, you don't have governance — you have assumption.
If you'd rather talk to a person about your situation, email info@trestano.com — you'll get a reply from someone who works on the product.
30-second check
Four questions, no sign-up, no email. You'll get a plain-English answer straight away.
1.Do you have customers or staff based in the EU?
Even a handful of EU customers or one EU-based employee counts.
2.Does any AI tool you use touch personal data?
Personal data means anything about a real person — customer emails, CVs, support tickets, HR records.
3.Does an AI tool make or influence a decision about a person?
For example: shortlisting job applicants, setting a price, deciding eligibility, or flagging an account.
4.Do customers interact with an AI tool directly?
A chatbot on your site, an automated email reply, or an AI-generated quote.
0 of 4 answered.
What makes Trestano different
Most providers sell a document or a tool. Trestano works across the full path — from first assessment to audit-ready evidence.
Assess organisational capability — the tools in use, the data they touch and the gaps in how they're governed today.
Define ownership, controls and accountability — a framework with named decision-makers, sized to a small team.
Inside the model →Operationalise governance — approvals, registers and records built into everyday work, not a binder on a shelf.
Why policies aren't enough →Prepare for ISO 42001 — evidence assembled continuously, so an audit or customer review finds you ready.
Ideal for
If AI is already part of how your organisation works — or is about to be — Trestano is built for you.
How it works
Assess organisational readiness, governance maturity and AI visibility.
Outputs
Design governance structures, ownership models and accountability frameworks.
Outputs
Validate that AI systems operate within approved authority and boundaries.
Outputs
Embed governance into day-to-day AI operations.
Outputs
Monitor effectiveness and continuously improve governance.
Outputs
Prepare for ISO 42001 and future regulatory expectations.
Outputs
Free, no credit card. Register your tools and get an instant risk picture before you commit to anything.
Start free — check your AI compliance status →Why governance matters
Data, risk, policy and business intent can change while an AI system is working. Trestano's runtime controls check authority again before action and preserve evidence of what happened.
Authority must remain valid at the moment the AI acts — not only when permission was first given.
Governance at Execution™ starts with Attributable Authority™: knowing who gave AI permission to act, what they delegated and where that permission ends.
Explore Attributable Authority™ →Read the Runtime Authority Continuity explainerGovernance at Execution™
Authority is checked, not assumed. Each control answers one question at the moment an AI system acts.
A new pillar: AI Ownership Governance
Organisations increasingly own intelligence: models, automations, decision systems, open-weights and fine-tunes. Ownership brings obligations — and accountability. This is not a technical question. It's a governance one.
Models, automations, decision systems, open-weights and fine-tunes — most businesses can't list what they actually own.
Regulatory, operational, economic, security and provenance duties follow the intelligence you own — whether you planned for them or not.
Named owners, update cycles, drift management and intervention rights — so no AI system operates without someone answerable for it.
Alongside authority boundaries, live oversight, reversible actions, consequential system mapping and operational intervention, "Own Your AI" is the natural extension of our core message: AI exposure is governance, not technology.
AI ownership governance review — from £1,450
A fixed-fee review that inventories the intelligence you own, maps the obligations it creates and names who is accountable for its behaviour. Optional ongoing oversight from £395/mo.
The governance landscape
AI governance is shaped by standards, risk models, security guidance and regulation — not one rulebook. The challenge is knowing where written requirements end and day-to-day oversight begins. Trestano translates that landscape into practical, accountable workflows.
The structure for an AI management system. Trestano helps turn its management requirements into assigned responsibilities, records and review cycles.
A common way to identify and discuss AI risk. We connect those principles to specific decisions, owners and oversight measures.
An emerging approach to autonomous agents that draws attention to boundaries, human intervention and evidence when agents act.
Risk-based obligations for AI systems in scope, including some uses by UK businesses. Trestano helps map relevant systems and organise the evidence needed for their governance.
Risks such as prompt injection, sensitive-data disclosure and unsafe agent behaviour need a place in governance reviews, alongside technical safeguards.
Leadership guidance explains why oversight matters. Trestano helps make it concrete: who owns each system, what gets reviewed and when to intervene.
These resources define the landscape. Trestano focuses on the operational reality: ownership, oversight, evidence and authority boundaries for AI systems, including autonomous agents. AI governance should be something your team can act on, not just a framework on a shelf.
AI governance, done for you
When a client, insurer or regulator asks for evidence, our add-on services cover the parts a template can't: vendor due diligence, outsourced DPO support, sector playbooks, staff training and ISO 42001 gap assessments — fixed fees, no day rates.
Pricing
£0
The free check and up to 3 AI tools recorded.
from £79
One-off. Unlocks your policy and assessment pack as PDFs.
from £49/mo
Unlimited tools, review reminders, incident log and rule-change alerts.
from £750
Hands-on setup, training and a review with a specialist.
Additional services
The Trestano platform registers and classifies your AI tools. These add-on services cover the parts that need a person: vendor reviews, regulator-specific playbooks, staff training, incident response packs and implementation sprints.
Add-on service
£195–£249
A completed supplier risk review for the AI tool you are about to buy — data processing, sub-processors, training-data terms and the contract clauses worth arguing over.
Learn more
Add-on service
£495
Async access to a compliance professional who reviews your register, answers your questions in writing and keeps your documentation defensible as things change.
Learn more
Add-on service
£175–£225
Templates, checklists and regulator expectations for your actual sector — recruitment, legal and professional services, retail, healthcare or financial services.
Learn more
Add-on service
£19
Short, UK-focused e-learning on acceptable AI use, shadow AI and reporting — with completion certificates you can put in your compliance file.
Learn more
Add-on service
From £750
A structured half-day remote workshop plus follow-up: we populate your register with you, classify every tool, produce tailored documentation and train the team.
Learn more
Add-on service
£249
A prepared workflow for the day an AI tool leaks personal data — who decides, what gets recorded, and the ICO notification drafted before the 72-hour clock runs out.
Learn more
Add-on service
From £4,950
A structured readiness review against ISO/IEC 42001, the AI management system standard, mapping what your register and documents already cover and what certification would still require.
Learn more
Add-on service
From £1,450
A structured review of the intelligence your business owns — models, automations, decision systems, open-weights and fine-tunes — the obligations that come with it, and who is accountable for how it behaves.
Learn more
Add-on service
£1,250–£1,650
A live, governed inventory of every system capable of consequential action — classified by risk state, with named owners, update cycles and a quarterly governance review.
Learn more
Add-on service
£1,750–£2,250
A structured model for how, when and by whom AI actions can be stopped, reversed or overridden — with triggers, escalation pathways, override authority and reversibility design written down.
Learn more
Pilot Programme Available
From £1,500
Assess whether AI systems remain governed at the point they take action, not just when they are approved.
Learn more
Early Adopter Programme Available
From £250/month
Provide independent and periodic assessment of AI governance effectiveness, operational controls and assurance readiness.
Learn more
Add-on service
£1,450–£1,950
A named-owner governance model for rented, hybrid and owned intelligence: accountability assigned per model, with AI Owner, AI Steward and AI Reviewer roles and documentation that is ready for a compliance question or an audit.
Learn more
Add-on service · ISO/IEC 42001
From £149
Define the boundaries of your AI Management System (AIMS) and map the tools, workflows and higher-risk systems that belong inside it, with a clear inventory aligned to ISO/IEC 42001.
Learn more
Add-on service · Leadership accountability
From £199
Create and operationalise your AI policy with leadership accountability, decision-making authority and budget allocation clearly defined — so governance becomes a functioning part of the organisation, not a paper exercise.
Learn more
Add-on service · ISO/IEC 42001
From £249
Structured AI risk and impact assessments, plus a compliant Statement of Applicability with clear justification for the controls you include and exclude — one of the most scrutinised areas of ISO/IEC 42001 audits.
Learn more
Add-on service · ISO/IEC 42001
From £99
Training modules, role definitions and a governance resourcing plan so your teams have the competence and awareness to manage AI safely — solving the common audit failure of 'no trained people assigned'.
Learn more
Add-on service · ISO/IEC 42001
From £199
Operational controls that stop AI systems going live before risk assessment — approval workflows, lifecycle management and deployment guardrails for safe, compliant adoption.
Learn more
Add-on service · ISO/IEC 42001
From £249
Structured internal audits, monitoring dashboards and management review support — findings that get acted on instead of tick-box audits that pass and change nothing.
Learn more
Add-on service · ISO/IEC 42001
From £149
Root cause analysis, corrective actions and continuous improvement cycles for your AI governance — so the same findings stop recurring, audit after audit.
Learn more
Governance bundle
£499
Everything an SME needs to begin its AI governance journey: a defined scope, a written AI policy, a single-tool risk assessment and staff awareness training — in one fixed-fee bundle.
Learn more
Governance bundle
£1,499
Full ISO/IEC 42001 alignment in one fixed-fee bundle: full scope mapping, leadership accountability, multi-tool risk assessment with SoA, lifecycle controls, internal audit and a corrective action plan.
Learn more
Governance bundle
£2,499
Everything in the Pro Governance Bundle plus the ongoing machinery auditors look for: management review support, quarterly monitoring, an annual scope refresh and a continuous improvement programme.
Learn more
Built for teams across UK sectors
The sectors Trestano is built for. No client logos are shown — Trestano is new, and its first engagements are being taken now.
Our ratings and templates follow ICO guidance (the UK's data protection regulator) and the EU AI Act's approach to risk. This is structured guidance and documentation — it is not legal advice, and it doesn't replace a solicitor where you need a formal opinion.
We built Trestano because most businesses can't answer one simple question: which AI tools does your business actually use? We're a small team focused on plain English, practical documents, and honest guidance.
Read more about usFree guides
What a workable staff AI usage policy has to cover, and how to write one.
Lawful basis, transparency and records when an AI tool touches personal data.
What the UK regulator actually expects from a small business using AI.
When serving EU customers pulls you into scope, and what changes if it does.
A step-by-step list of the obligations by risk category.
ICO, FCA, EHRC, MHRA and more — who oversees what.
Everything below comes out of the register you build in ten minutes — no separate briefs, no document chasing.
The compliance check is free, and you'll leave with a clear list of what to fix first.
Check your AI compliance statusThe Trestano AI Governance & Readiness Diagnostic™ measures where you stand across five dimensions — and gives you a prioritised plan for what to do next.
Book a Diagnostic